01 / Executive brief
Executive summary
The United States alleged that from 2011 through 2018, officers of the Hainan State Security Department—a provincial arm of the PRC Ministry of State Security—used Hainan Xiandun Technology Development Company as a front to recruit and manage hackers. Four named defendants were charged with a campaign targeting companies, universities, research institutes, governments, and other organizations. S1 S3 S5
The alleged target list read like a strategic technology portfolio: submersibles and autonomous vehicles, aircraft servicing, chemicals, genetic sequencing, Ebola research, and railway information, among other sectors. U.S. agencies and the United Kingdom's National Cyber Security Centre publicly attributed the activity to APT40 and published technical indicators, but the indictment has not produced trial findings; the named individuals are presumed innocent unless proved guilty. S2 S4 S5 S6
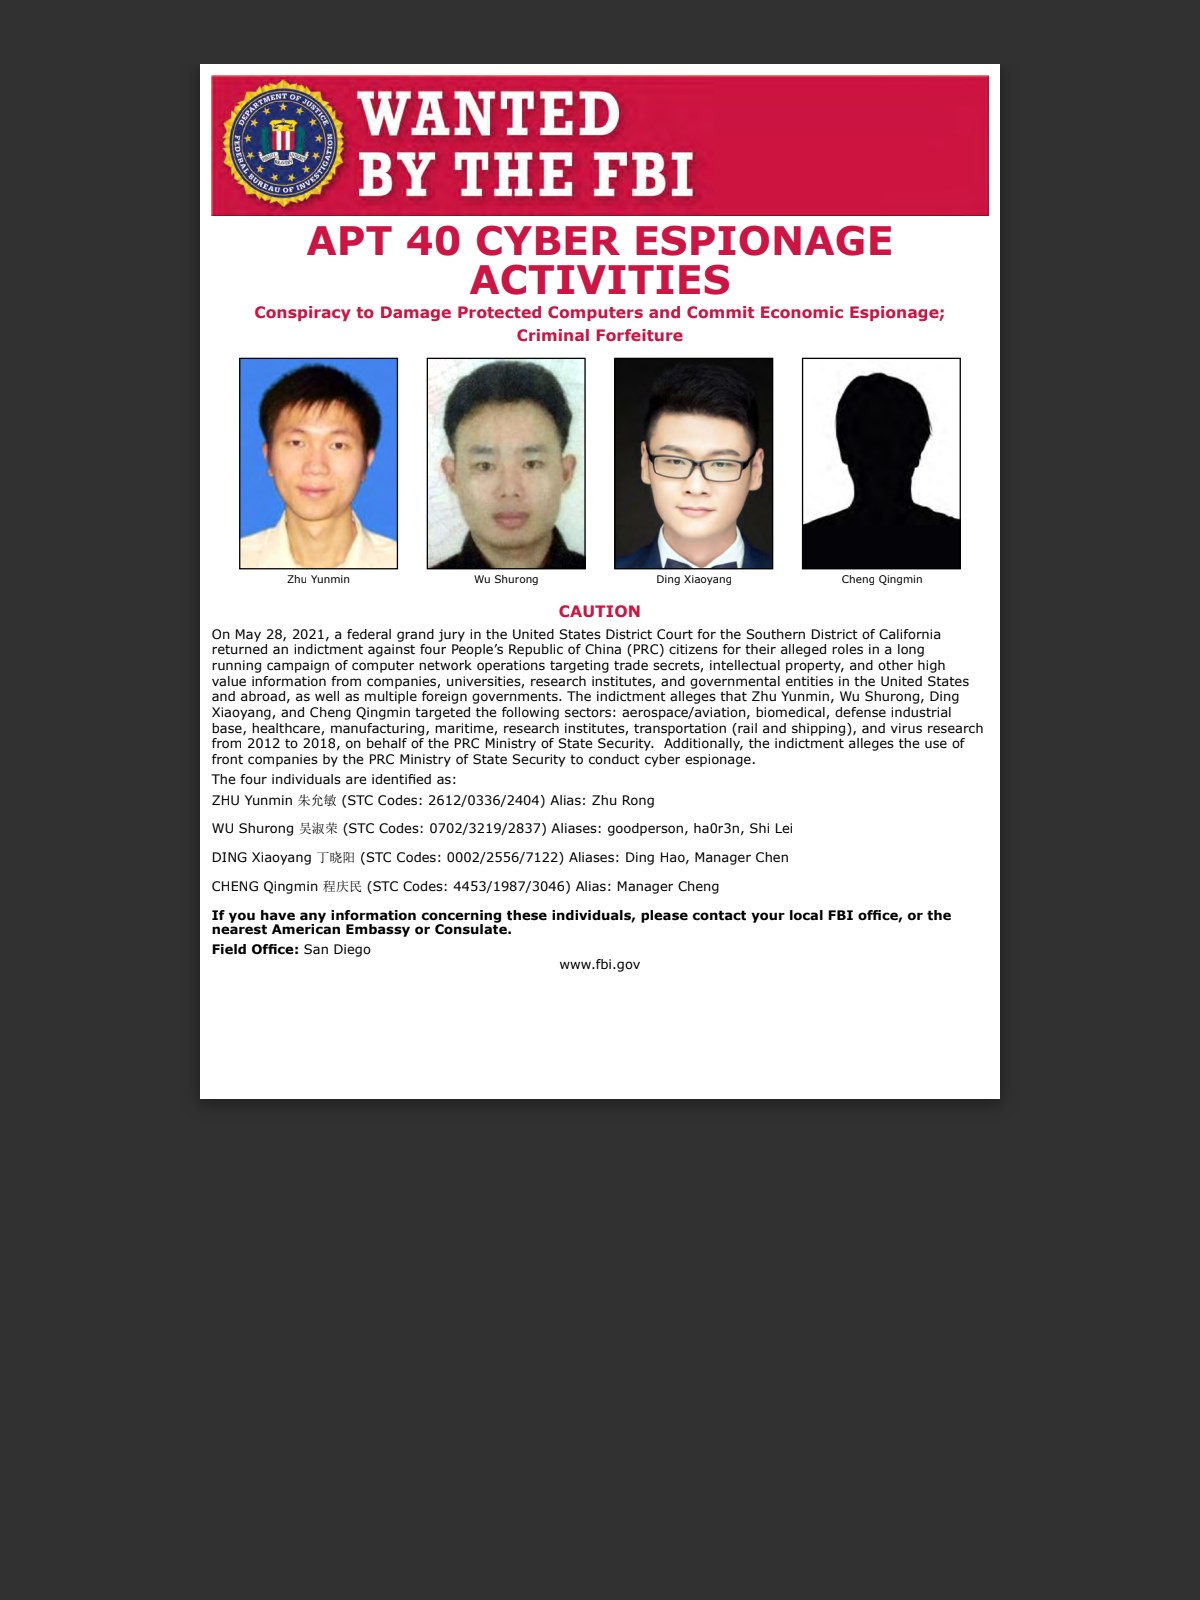
The FBI's official APT40 poster identifies Zhu Yunmin, Wu Shurong, Ding Xiaoyang, and Cheng Qingmin; no photograph is shown for Cheng. A wanted poster records accusations, not convictions.
Federal Bureau of Investigation · Public domain U.S. government work ↗02 / The vignette
What happened
A front company supplied the operating layer
According to the indictment, Hainan intelligence officers coordinated hackers through Hainan Xiandun rather than operating only under visible government names. The company allegedly helped recruit technical personnel, provide a workplace, and give state-directed activity a commercial exterior. S4 S5
The campaign followed useful technologies
Victims were not confined to one defense contractor or one country. Prosecutors alleged intrusions against dozens of organizations in at least twelve countries and identified targets spanning maritime systems, aviation, biomedicine, transportation, and research. That breadth is the central vignette: cyber access can be managed as a continuing collection program rather than a one-company theft. S1 S2 S5
Attribution is not adjudication
CISA, the FBI, and the United Kingdom's National Cyber Security Centre released attribution statements or technical advisories linking tools and methods to APT40, while the FBI published a wanted poster naming Zhu Yunmin, Wu Shurong, Ding Xiaoyang, and Cheng Qingmin. Those are official allegations and attributions. Because no cited judgment establishes guilt, this file uses allegation language throughout and does not count the case as adjudicated. S2 S3 S4 S6
03 / Anatomy
How access became transfer
This six-part framework asks the same questions of every file. Each stage carries its own evidence state; a listed stage can be alleged, inferred, interrupted, disputed, or not established. The structure does not manufacture a completed transfer or harm.
- 01
- 02
- 03
Acquisition assessed Officially alleged or attributed
Strategic data targeted
The indictment alleged collection from technology, research, government, and industrial victims. S5
- 04
- 05
Downstream use assessed Not established
Intelligence objective attributed; downstream use not established
U.S. and allied authorities attributed the campaign to a PRC intelligence bureau seeking strategic and commercial information, but the cited record does not establish how any acquired information was later used. S2 S5 S6
- 06
04 / Evidence boundary
What is established—and what is not
Established in the record
05 / Sequence
Timeline
06 / People and institutions
Who appears in the public record
Zhu Yunmin
Hainan State Security Department officer named in the indictment S1 S2 S3 S4
Wu Shurong
Ding Xiaoyang
Hainan State Security Department officer named in the indictment S1 S2 S3 S4
Cheng Qingmin
Hainan State Security Department officer named in the indictment S1 S2 S3 S4
Hainan Xiandun Technology Development Company
Alleged front company used to recruit and support hackers S1 S2 S3 S4
Originator / affected institution
Targeted companies, universities, and public institutions
Creators and custodians of the allegedly targeted technology and data S1 S2 S3 S4
07 / Consequences
Documented, attributed, potential, and unknown consequences
Authorities alleged intrusions against dozens of organizations in at least twelve countries, but the public record does not quantify verified losses across the campaign. S5
08 / Hindsight analysis
Where leadership could have seen risk
These are our analytic judgments based on the public record, not court findings. They are framed to improve controls without treating nationality as a risk factor.
One campaign crossed many sectors
Organizations evaluating only sector-specific criminals could miss infrastructure and methods reused against unrelated technology portfolios.
Commercial cover obscured sponsorship
A contractor-style company allegedly supplied recruiting and operational support while shielding an intelligence relationship.
09 / Apply the lesson
Actions leaders can take
- both
Use current government indicators
Map CISA and FBI indicators and techniques to telemetry, identity systems, vulnerability management, and incident-response playbooks.
- both
Share cross-sector signals
Participate in sector and government information-sharing channels so repeated infrastructure is visible beyond one institution.
- both
Preserve attribution limits
Separate observed technical behavior, official attribution, charged allegations, and court findings in every executive briefing.
10 / Source record
Sources
Links point to the public record reviewed for this file. Government releases can summarize court proceedings but remain government-authored sources; the source note identifies those limits.
- S1 official attribution government release
Four Chinese Nationals Working with Ministry of State Security Charged in Global Computer Intrusion Campaign ↗
U.S. Department of Justice · Published Jul 19, 2021 · Retrieved Aug 23, 2026
Charging allegations; defendants are presumed innocent.
- S2 official attribution government release
U.S. Government Releases Indictment and Advisories Detailing Chinese Cyber Campaign ↗
Cybersecurity and Infrastructure Security Agency · Published Jul 19, 2021 · Retrieved Aug 23, 2026
- S3 official attribution government release
APT40 Cyber Espionage Activities Wanted Poster ↗
Federal Bureau of Investigation · Published Jul 19, 2021 · Retrieved Aug 23, 2026
- S4 official attribution government release
Tactics, Techniques, and Procedures of Indicted APT40 Actors Associated with China's MSS Hainan State Security Department ↗
Cybersecurity and Infrastructure Security Agency · Published Jul 19, 2021 · Retrieved Aug 23, 2026
- S5 procedural record court record
Indictment: United States v. Ding Xiaoyang, Cheng Qingmin, Zhu Yunmin, and Wu Shurong ↗
U.S. District Court for the Southern District of California via U.S. Department of Justice · Published May 28, 2021 · Retrieved Aug 25, 2026
Locator: United States v. Ding Xiaoyang et al., No. 3:21-cr-01142, ECF No. 1
Certified charging document supporting the named defendants, alleged Hainan State Security Department and Xiandun roles, charged period, targets, and alleged conduct; it is not a finding of guilt.
- S6 official attribution government release
UK and allies hold Chinese state responsible for a pervasive pattern of hacking ↗
United Kingdom National Cyber Security Centre · Published Jul 19, 2021 · Retrieved Aug 25, 2026
Allied attribution statement supporting the description of coordinated U.S. and partner attribution; it does not adjudicate the individual defendants' guilt.
12 / Reference
Cite this dossier
Use the permanent URL and review date below so readers can identify the version of the public-source record you consulted.
ChinaSteals. “A Hainan intelligence bureau allegedly used a front company to run a global technology-hunting campaign.” CS-025. Published Aug 23, 2026; last reviewed Aug 25, 2026. https://chinasteals.com/cases/apt40-hainan-mss-campaign/